HUGE security flaw

caseybot··29 votes·11,963 views

So ever since the new launcher came out I have been quite a fan of it. However, that all changed when someone got access to my account. I'm not exactly sure how they did it but they managed to play multiple games on my account. Once I figured this out I changed my password immediately. I thought the problem was over and I didn't have to worry anymore. I quickly found out I was wrong. When I launched the game to enter my new password, It immediately sent me to the home screen. I thought it was a little odd at first so I waited to see if the password hadn't been updated yet. After hours of waiting it still just let me log in automatically without having to enter the new password. I changed my password again to see if it fixed it and once again, it did not ask me to enter my new password. The person who originally took of my account still has access and is still playing games and I have no way to get them off my account. I have emailed riot support however they seemed to ignore it and just prompt another password change. This is a huge security flaw and needs to be addressed immediately.
20 Comments

Silent Pace6 votes

You might want to try enabling two factor authentication. You will then be able to remove the player that's using your account from a trusted accounts list. https://support.riotgames.com/hc/en-us/articles/360010367273-Two-factor-authentication-FAQ I'm not sure if this will solve the problem but I hope it does.

caseybot3 votes

[{quoted}](name=Silent Pace,realm=NA,application-id=LqLKtMpN,discussion-id=tHTMBxxb,comment-id=0003,timestamp=2019-11-14T05:07:45.342+0000)

You might want to try enabling two factor authentication. You will then be able to remove the player that's using your account from a trusted accounts list. https://support.riotgames.com/hc/en-us/articles/360010367273-Two-factor-authentication-FAQ I'm not sure if this will solve the problem but I hope it does.

That's actually a good idea. Thank you for the suggestion, I will do that right now. I hope that will solve the issue.

Honeydew Zekling2 votes

{quoted}

That's actually a good idea. Thank you for the suggestion, I will do that right now. I hope that will solve the issue.

Two factor authentication is really the best way to make sure your account doesn't get hacked into. I understand why Riot doesn't force everyone to use it (Don't yall have phones??), but it really acts as that final gatekeeper.

The other thing you brought up is highly concerning. The fact that a password change isn't prompting the client to ask you to re-authenticate and enter the new password is a huge red flag. Sounds like they are just using a login token that never really expires. If you haven't already, create a support ticket and highlight this. Someone guessing your password is one thing, having a password change not force users to enter the new password is definitely a bug (and security exploit)

MagicFlyingLlama2 votes

Check your email account for any odd activity and reset the password on that.

Balderdash100020 votes

{quoted}

Check your email account for any odd activity and reset the password on that.

You're not getting the complaint. If you change your password on league it doesn't sign you out of the account. You can keep playing on any computer that you had already signed in on with the previous password without knowing the new one. It's pretty bullshit as far as security goes.

caseybot11 votes

{quoted}

You're not getting the complaint. If you change your password on league it doesn't sign you out of the account. You can keep playing on any computer that you had already signed in on with the previous password without knowing the new one. It's pretty bullshit as far as security goes.

Exactly the issue.

MagicFlyingLlama4 votes

The huger security flaw is that the password got stolen in the first place.

Terozu2 votes

Passwords can be guessed super fucking easily on any platform not just league. That's not something you can really help.

Literally your bank is no more secure than your league account password wise.

Trias0002 votes

{quoted}

Passwords can be guessed super fucking easily on any platform not just league. That's not something you can really help.

Of course you can - you can use more secure passwords.

Terozu1 votes

There's really no such thing.

OoC what would you define as a secure password?

Anidan2 votes

10+ characters with non-alphanumeric characters thrown in. If you're logging onto a system that doesn't allow non-alphanumerics, then the longer you make it, the better. Most login systems lock you out after enough failed attempts, and somebody being able to successfully guess a password of the length I mentioned with non-alphanumerics thrown in is next to impossible within the lockout attempt window. Alphanumeric characters give you a possibility of 36 characters per password character to choose from, add in non-alphanumerics and you get significantly more.

Even if you were to take a general password, like the stereotypical "Password123," you could do "P[as]s/w-or=d1,2(3" and you've made it significantly harder to crack, even for a password that started off that simple. The only reliable way someone is getting that password is if they use a program to brute force passwords in a system that doesn't lock you out from repeated failed attempts, or decrypt the password database (which is a huge undertaking in and of itself), or scam it out of you.

Trias0001 votes

{quoted}

There's really no such thing.

OoC what would you define as a secure password?

kfdj#($ K# LL@#(#$ #DFDLdsafd#$(#@(sfaas#$))##_@_DFda#+$#++@$#+##+fdsaFDKJF:LKJDS(#($#(#$ (#O KEKRfafomegalulRK< $)#)#

MagicFlyingLlama2 votes

If you make your password 5 letters long, yes. Every additional letter multiplies how hard it is to guess by the number of possible characters.

A LoL password can be up to 30 chars long, alphanumeric at the least, so a minimum of 36 possible chars.

According to the handy scientific calculator in windows, 30^36 is 1.50094635296999121e+53, which i wont write in normal notation because it is over 50 digits long. That is the number of possible passwords.

A decently long password with a scattering of non-alphanumeric is utterly impossible to guess even if the server does not lock out the account after multiple failures, which most do.

Basically all league "hacks" are because someone gave away their login info on some "Free RP" scam or had their email stolen in a similar fashion. Of course people rarely admit to something that moronic.

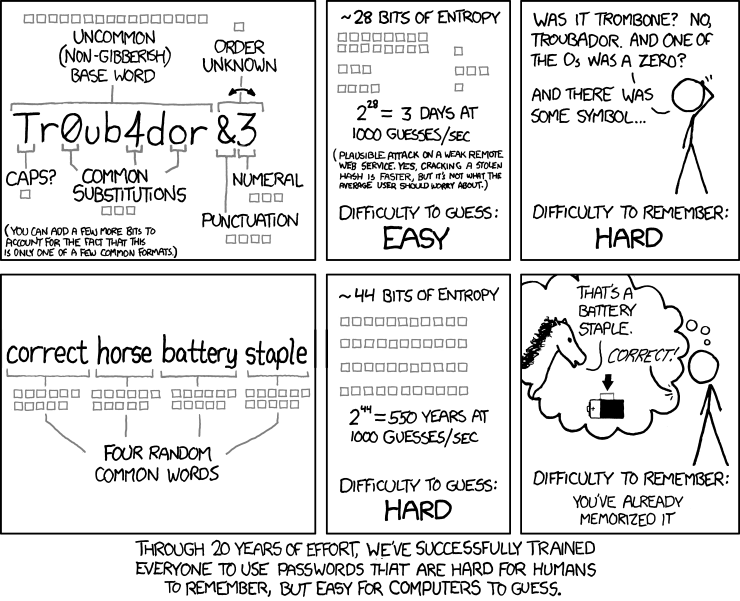
Relevant XKCD https://imgs.xkcd.com/comics/password_strength.png

caseybot2 votes

{quoted}

Check your email account for any odd activity and reset the password on that.

I checked my email and there were no other log ins other than mine but I did reset the password on it to be safe and changed my league password again and the person still has access. Thank you for the advice though.

Lordofthepittt2 votes

At least you still have your account. My friend lost his account because someone jacked it, hacked a bit and then Riot auto banned it, and refused to listen to him when he tried to get the account back and explained the situation.

To be honest Riot is really really good at security and intelligent bans.

SpookyNeedle1 votes

When you exit the client you gotta click the Sign Out button and then when prompted to login at launch make sure you don’t have “Remember me” on. If that doesn’t fix it idk

caseybot8 votes

{quoted}

When you exit the client you gotta click the Sign Out button and then when prompted to login at launch make sure you don’t have “Remember me” on. If that doesn’t fix it idk

That would only sign me out. It still would not prompt the other person who took my account to put the new password in.

Trias0001 votes

Riot, what the actual fuck? This is probably the dumbest of your dumb mistakes. And there's been plenty. https://i.memeful.com/media/post/QRyv0dv_700wa_0.gif

Diopsideˆ1 votes

When 2FA coming to League, when Riot?

XJ999999999999991 votes

small indie company.

prob gonna take 3-4 years just like the ability to change email/pass without going to the actual email, lmao.

More from Report a Bug